Designing Human Approval Gates for SitecoreAI Content Workflows
A human approval gate is useful only when the human can identify the proposed effect and the system executes within that decision. A button labeled Approve is not enough information. The reviewer needs to know which content revision they are accepting, where it will go, and whether their decision permits drafting, updating, publishing, or an external action. The execution path needs a way to check that those facts still hold when work resumes.
Sitecore documents an Approval action that pauses a workflow until a human reviews and approves. That is a useful building block, not a substitute for defining the organization’s approval contract. This article proposes that contract for a hypothetical SitecoreAI campaign workflow. The examples describe integration-owned records and acceptance exercises. They are not importable workflow definitions, customer incident reports, or claims that the native action provides every control discussed here.
My position is that approval should attach to a specific proposed effect rather than a general conversation status. That creates revision-management work, especially when reviewers ask for changes. I would accept that cost for shared or public content because it makes the eventual action explainable. For disposable drafts, a lighter process may be sufficient. The right gate follows the consequence of the action and the evidence a person must inspect.
1. Define what the reviewer is actually approving
Separate content review from permission to act
Begin by naming the decision. A copy editor might approve tone and readability without authorizing a public release. A campaign owner might approve a destination change but not an external notification. A publisher might authorize release only after the required content review is complete. The organization can combine these responsibilities where appropriate, but it should not let one ambiguous approval flag stand for all of them. Write the permitted effect in language the reviewer understands and the execution service can evaluate.
Sitecore’s workflow action reference describes Approval as a human-in-the-loop pause. Its spaces guidance describes flows that combine agent-driven and human-assisted work. Use those documented capabilities as the starting point for the deployed process. Confirm the actual configuration surfaces in your tenant before implementing any example. The proposed approval packet below supplies application requirements; it does not assert additional native action parameters.
For the hypothetical campaign, list the consequential transitions. Generating a private proposal is one transition. Writing a draft into a shared destination is another. Publishing or sending a message is a separate effect. Decide where the organization requires a person to intervene. Avoid placing a gate before every small generation step simply because the workflow supports pauses. A gate should protect an identifiable decision. Otherwise reviewers may spend time approving intermediate text without seeing the destination change that actually matters.
Scope the decision by resource and revision
For each protected transition, identify the destination resource, requested operation, language, and content revision. A statement such as “approve this campaign” leaves room for disagreement about whether a later localized page or new audience is covered. In this design, those changes create a new approval subject unless policy explicitly permits them. The policy owner should define that scope before execution. Do not let the model decide that a new destination is sufficiently similar to inherit a previous authorization.
Define which assumptions are part of the approval. A reviewer might rely on an approved product specification, a current offer, or a particular destination version. Record the references needed to assess those assumptions later. An approval does not need to copy every source document, but it should retain enough context to explain the decision. If a source changes while the run waits, the execution process needs a policy for determining whether the old decision remains valid or needs renewed review.
Distinguish a recommendation from an authorization. A generated reviewer summary may say that content is ready. A confidence score may suggest that a field aligns with the available context. Neither should create the trusted approval record in this proposed architecture. The relevant human or authorized service must make the decision through the supported mechanism. Keep generated evaluations available as evidence, with their limitations visible, rather than allowing them to write the status that grants permission to perform the consequential action.
Choose the smallest sufficient gate
Match the review burden to the consequence. A draft-only workflow might require a content owner to accept an artifact before it enters a shared library. A public campaign change might require an additional release decision. A regulated or contract-sensitive claim may need specialized review under the organization’s existing policy. These are examples of policy choices, not legal advice or universal Sitecore requirements. The architecture should support the chosen responsibilities without pretending that one approval scheme fits every content operation.
Use an approval matrix that lists the action class, eligible decision maker, required evidence, and invalidation conditions. Review the matrix with editorial and engineering owners together. A process diagram alone can hide that the person assigned to a gate lacks permission over the target or cannot inspect a necessary source. Resolve those gaps before automating. The matrix should also say whether a substitute reviewer is permitted and how delegation is recorded. Do not make reviewer availability an excuse for silently broadening authority.
Specify the outcome of an incomplete review. A reviewer may accept the wording but flag an unresolved product claim. The workflow should represent that result as a limited decision or a return for correction, according to policy. A free-text comment saying “looks fine except the offer” should not be parsed into an unrestricted approval by another model. Provide explicit decision options whose meaning is documented. Comments add context; they should not be the only machine-readable representation of what the reviewer authorized.
The acceptance exercise for this stage is a conversation with two reviewers who have different roles. Give them the same draft and ask each what their approval permits. If the answers differ from the intended execution behavior, revise the gate description. Then ask an operator to identify the next permitted action from the recorded decision. A sound gate should communicate the same scope to the reviewer, the implementation, and the person who later diagnoses a waiting or failed run.
2. Build an approval packet tied to a revision
Make the proposed change inspectable
Prepare one review packet per proposed effect. Include the content revision, destination, requested operation, important evidence references, and unresolved questions. Show the difference from the destination state the workflow read when that matters. For a new page, show the proposed structure and where it will be created. For an update, show the changed fields rather than requiring the reviewer to find them inside a long generated article. The packet should make disagreement possible without asking the reviewer to reconstruct the entire agent conversation.
Keep the packet distinct from the evolving drafting workspace. Sitecore’s artifact management documentation describes editing and revision comparison. Use the supported artifact versioning surfaces when preparing a review, and preserve a stable reference in your integration where the interface permits it. If the selected route cannot reliably bind a decision to a native revision, document a controlled packet or export process. Do not manufacture a native revision identifier merely to make the application record look complete.
For the hypothetical localized campaign, the packet might show an approved headline, a destination-language summary, a proposed call to action, and the source of an offer claim. The reviewer should see which material is copied from approved evidence and which wording is newly generated. Distinguish missing evidence from low stylistic quality. A beautifully phrased offer with no approved basis should not pass merely because the packet’s overall quality score is high. Make the unresolved claim visible at the place where the decision is made.
Bind the decision to a stable subject
The following JSON is an illustrative application record. It is not the schema of Sitecore’s Approval action. The packet reference identifies the proposed effect; the decision record links an authorized reviewer to that subject. The implementation must determine the actual identifiers and supported storage mechanism.
{
  "packetRef": "campaign-change-packet-17",
  "artifactRevisionRef": "reviewed-artifact-revision",
  "destinationRef": "verified-target-item-and-language",
  "effect": "update_draft",
  "decision": "approved",
  "reviewerRef": "authenticated-reviewer-reference",
  "policyRevision": "campaign-review-policy-3"
}
Compute any content digest from a precisely defined representation if your integration uses one to detect changes. Record whether the digest covers visible text, field assignments, source references, or the complete packet. A digest of the article body alone would not detect a changed destination if the destination is outside that representation. Do not call a packet unchanged unless the comparison covers the facts that determine authorization. Preserve a readable revision reference alongside technical integrity evidence so people can understand what they are inspecting.
Define which edits create a new packet. A changed destination, audience, claim, or requested action should be considered explicitly. The policy may permit a constrained class of cosmetic corrections without a full new review, but that class should be described and enforced. Avoid giving the drafting model authority to declare its own changes harmless. If an edit falls outside the permitted transformation, create a new revision and request a new decision. Preserve the old packet as history rather than rewriting it under the existing approval record.
Keep the review interface focused
Show the reviewer the decision first: what will change and what accepting it permits. Place supporting evidence where it can be opened without losing the review context. Show unresolved questions prominently rather than hiding them in the final paragraph of a generated assurance. For a presentation-sensitive change, provide the supported preview surface. For a content-only field update, a focused difference view may be more useful than a full page preview. Choose based on what the reviewer actually needs to judge.
Avoid overwhelming the packet with every intermediate prompt and tool result. Retain diagnostic references for operators, but give reviewers a concise path through the evidence. If a tool warning matters to the decision, translate it into a clear issue while retaining the original reference. Do not remove uncertainty merely to keep the interface clean. A packet with one visible unresolved claim is more useful than a summary that says everything is ready while the underlying run contains a warning no reviewer will discover.
Record rejection reasons in categories that support correction. For example, the reviewer might reject a source claim, a destination choice, or the requested action scope. Free text can explain the case, while the explicit category routes work to an appropriate stage. These are proposed application categories. The purpose is to avoid returning every rejection to a generic rewrite step. A wrong target needs target resolution, not more fluent copy, and a missing permission needs an authorization decision rather than a different prompt.
Test the packet with a reviewer who did not help build the workflow. They should identify the exact revision, the destination, the unresolved issues, and the effect of each decision option. Ask them to reject one issue and verify that the next stage addresses that issue without altering unrelated approved facts silently. This rehearsal checks whether the packet communicates the decision. It does not prove that the execution boundary enforces the decision; that needs separate implementation and testing.
3. Enforce authority at the execution boundary
Enforce the gate where effects occur
An approval record should be checked by the trusted component that performs the protected operation. In a custom integration, that component should validate the packet identity, the decision, and the permitted action before issuing the destination request. It should also use the authenticated execution context required by the actual interface. Do not let generated content supply the identity of the approving user or declare that a permission check passed. Those are facts the trusted application must establish independently of the model’s narrative.
Sitecore’s workflow configuration guidance discusses content approval roles and warns that administrator users can bypass ordinary workflow behavior. That matters when choosing execution identities. A workflow service with broad privileges may be able to act beyond the review scheme shown to editors. Inspect the actual identity and destination permissions. Do not assume that placing an Approval action on the canvas automatically restricts every external connector or service identity that runs afterward.
Apply least privilege to the action surface. OWASP’s Excessive Agency guidance identifies excessive functionality, permissions, and autonomy as risk factors. For this design, separate a drafting capability from a release capability where the deployment supports that boundary. If the same connector exposes unrelated destructive or disclosure actions, assess whether a narrower service is appropriate. A trusted gate should limit what can happen even if an untrusted document persuades the model to ask for something else.
Revalidate the facts that can expire
Check authority when the decision is made and again when executing if the process can wait long enough for relevant permissions to change. A reviewer might leave a role, a campaign might be withdrawn, or the destination might move outside the approved scope. Define which of those changes invalidates the decision. Where the native mechanism does not expose a needed check, keep it in a supported integration or manual release procedure. Be explicit about that boundary rather than claiming a capability the platform documentation does not establish.
Recheck the destination assumptions before writing. Prefer a documented conditional update or concurrency control if the selected interface provides one. A separate read-before-write check may detect a conflict but leaves a race before the actual update. The admitted limitation is that a read-before-write check does not create an atomic approval-and-write transaction. For consequential changes, use an available supported locking or conditional mechanism, or choose a controlled human process that accepts and manages the remaining risk. Do not label a best-effort comparison as a guarantee.
Protect against a changed payload after approval. The component executing the action should compare the actual intended effect with the approved packet, using the defined revision or digest contract. That comparison should cover the destination and operation as well as content. If the effect differs, stop or request renewed review. A model-generated explanation that the new content is equivalent should not override this check. If policy permits a particular transformation, implement that permission as an explicit rule with test cases.
Preserve the boundary across integrations
For an external action, determine what the downstream interface actually confirms. An accepted request may not demonstrate that the intended business effect completed. Record acceptance and verification separately in the application state model. The approval permits a defined attempt under defined conditions; it does not automatically prove the outcome. A later read or delivery confirmation may be needed according to the operation. Avoid telling the reviewer that content shipped when the only evidence is that a request was submitted.
Keep operation identity stable when recovering the same approved effect. A retry should not create a new authorization scope or silently substitute a newer artifact. If the downstream system supports documented idempotency, follow that contract. If the result is uncertain and cannot be reconciled reliably, route it to an operator. The approval packet should remain attached to the original intended action so the operator can compare what was permitted with what may have happened. Recovery is not permission to broaden the task.
Log decisions at a useful level without copying unnecessary sensitive material. Record packet references, authenticated actor references, policy revisions, and state transitions. Retain source documents and detailed payloads under the organization’s normal access controls. An audit log full of raw credentials or private campaign material creates another governance problem. The execution record should let an authorized operator answer what happened and why, while ordinary reviewers receive only the evidence appropriate to their role.
The acceptance condition for the enforcement boundary is negative as well as positive. A valid packet with a permitted identity should allow the defined effect. A copied packet aimed at a different destination should fail. A revoked identity should fail according to policy. A changed payload should trigger the agreed invalidation path. These checks demonstrate that the gate constrains the action, rather than merely adding a ceremonial pause to a process that could perform the same action without meaningful authorization.
4. Design the waiting, rejection, and escalation paths
Model waiting as an operational state
A workflow that pauses for approval creates work that someone must own. Name the owner of the pending review and the owner of technical recovery. They may be different people. The reviewer decides whether the proposed effect is acceptable; the operator investigates why a decision was not recorded or why execution did not resume. Avoid a single status such as pending that leaves both groups unsure whether they should act. Use states that explain the next decision and show the relevant evidence reference.
For the hypothetical campaign, define an application progression such as prepared, awaiting decision, rejected, approved for a specific effect, executing, and verified. Include expired, cancelled, and uncertain outcomes if the process needs them. These are proposed state names, not native Sitecore workflow states. Document the permitted transitions and the component authorized to make each one. A generated sentence should not move the record into approved. A transport timeout should not move it into rejected. Each transition should represent a specific event or decision.
Determine what is durable across restarts for the exact mechanism you deploy. Preserve the review packet, decision, and operation reference where the supported interface or your integration stores them. Do not infer that a custom variable survives merely because the workflow has a pause action. Test a restart while waiting and after a decision but before an effect. The recovery procedure should identify the last confirmed state and avoid asking the reviewer to approve a different packet under the appearance of resuming the original review.
Make rejection lead to the right correction
A rejected claim should return to evidence correction or drafting. A rejected destination should return to target resolution. A rejected release time should return to campaign scheduling. Treat these as different work items when their owners differ. Re-running the entire workflow may erase useful context or repeat completed side effects. A correction stage should preserve the rejection reason and create a new packet revision. The reviewer should be able to compare the corrected proposal with the one they previously rejected.
Define what happens to earlier partial approvals. If the process has several independent decisions, one rejection may invalidate only a subset or may require a full new packet. The policy should explain that relationship. Do not compose independent approvals into a release permission unless their subjects and assumptions are compatible. An approval for one language and an approval for a different revision do not automatically combine into authority for a new localized artifact. The execution service needs a clear rule for the exact effect it is about to perform.
Allow reviewers to request clarification without pretending they approved or rejected the content. A missing source or ambiguous destination may require another owner to answer a question. Preserve that condition visibly. If your chosen workflow surface has only limited decision states, use a supported surrounding process to represent the additional work. Do not hide clarification requests in comments and have a model guess whether a polite response means approval. The purpose is to make the next required decision explicit.
Handle deadlines without manufacturing consent
Set review deadlines and escalation rules appropriate to the campaign. A deadline should determine who is notified or what work expires; it should not silently convert absence of a decision into approval. If the organization has a preauthorized automated policy for low-risk actions, describe that policy directly rather than calling it human approval. Keep the distinction visible in records. A reviewer who never examined the packet should not appear as the person who accepted it merely because they were assigned the task.
When a delayed approval arrives, check whether the packet remains eligible. The launch window may have passed, the source offer may have changed, or the destination may have a newer revision. Decide which changes require a fresh review and communicate that outcome to the reviewer. Do not make late approval an instruction to execute outdated work immediately. A valid decision in one context can become inapplicable when the effect or assumptions change. The workflow should preserve the original decision while recording why it no longer authorizes execution.
Plan delegation with the same care as the original assignment. A substitute reviewer should have the appropriate authority and access to evidence. Record who actually made the decision, not only the name of the person originally assigned. If a delegation expires, define what happens to the pending packet. Avoid forwarding raw sensitive content through an improvised channel just to obtain a quick response. Use the organization’s approved review route and make the delegation visible to the operator responsible for release.
The handoff exercise for this stage should include a waiting packet, a rejection requiring evidence correction, and an approval that arrives after expiration. An operator should locate the owner and the permitted next action in each case. A reviewer should understand why a new decision is required after the packet changes. If the team needs private knowledge from the original builder to resolve the exercise, improve the state model and runbook. Waiting work should be understandable as ordinary operational work, not as a mystery hidden inside a paused agent.
5. Test race conditions and misleading approval signals
Test invalidation rather than only the happy path
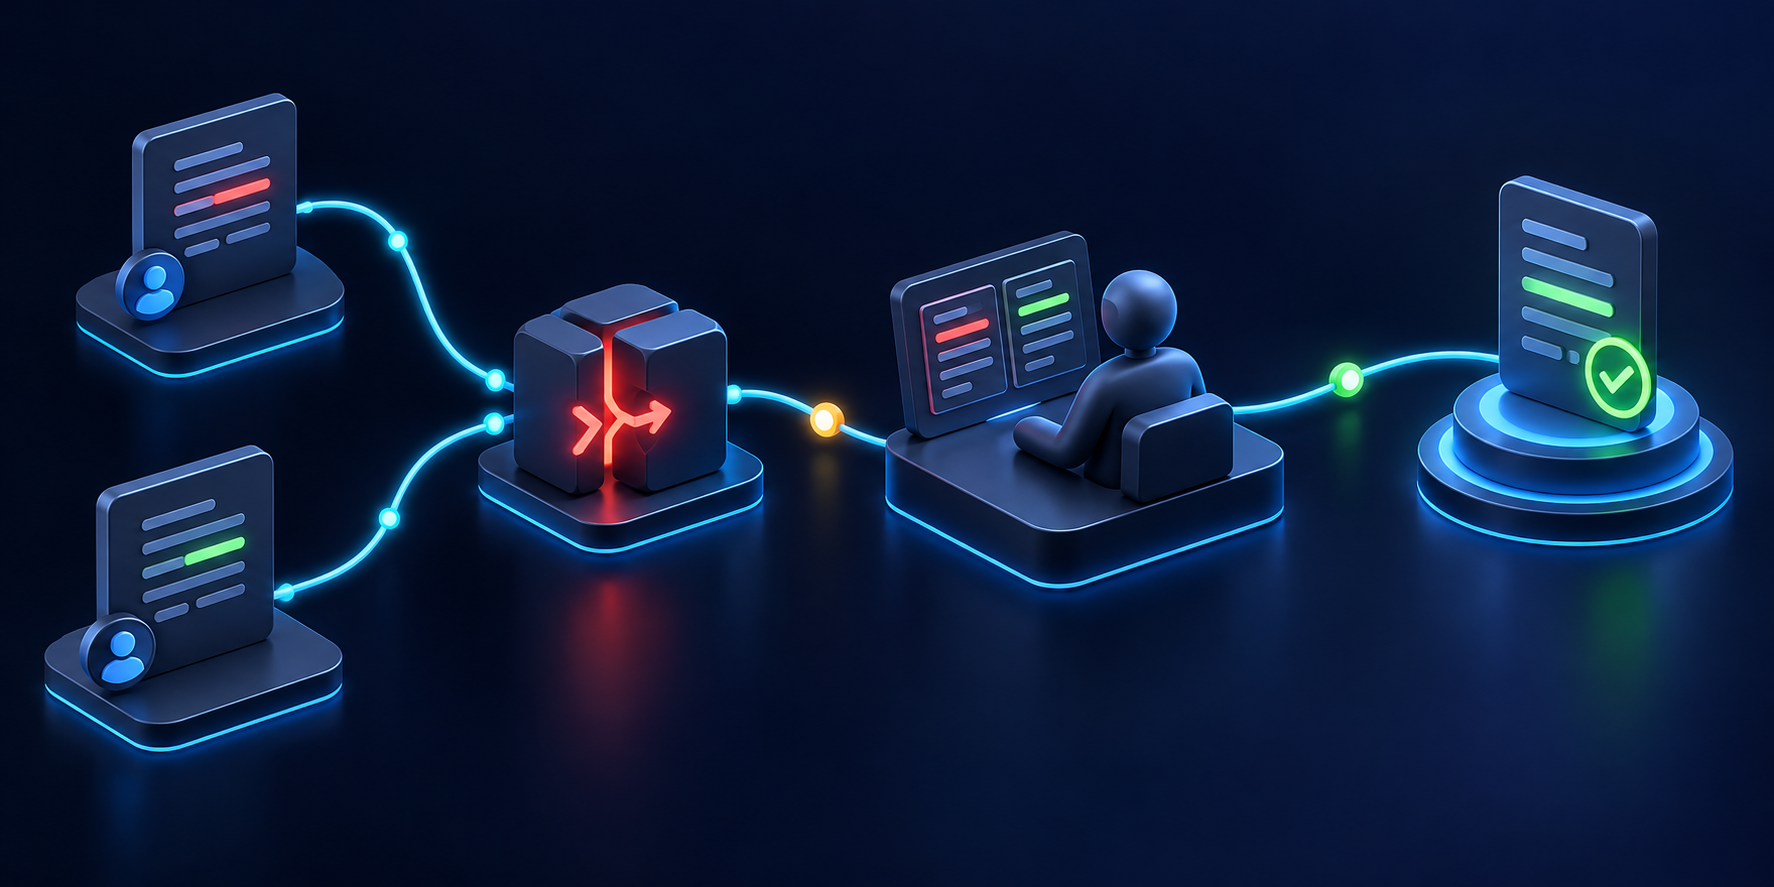
A successful click-through test demonstrates that one reviewer can approve one packet under one set of conditions. It does not demonstrate that approval cannot be reused incorrectly. Build fixtures around the boundary you intend to protect. The expected result should state whether the operation proceeds, returns for review, or stops for operator resolution. Define those outcomes before running the fixtures. Otherwise the team may rationalize whatever the system does as acceptable after seeing a polished result.
Start with a changed-artifact fixture. Prepare a packet, approve it, then create a different content revision before execution. The operation should follow the documented invalidation policy. Repeat with the same text but a different destination or language. That variant checks whether the approval binds the full effect rather than only a body-text digest. Include a changed operation class, such as moving from updating a draft to publishing. An approval for one class should not silently grant authority for another.
Add a concurrent-edit fixture. Let an editor modify the target after the packet is prepared. Use the actual destination interface and inspect the outcome. If a documented conditional mechanism is available, verify its conflict behavior. If the process relies on a controlled release window instead, rehearse that procedure. The test should make the remaining limitation visible. Do not report “concurrency protected” merely because an application performed a comparison before making an unconditional write through a separate request.
Exercise authority and evidence failures
Test a reviewer who lacks the required role and a reviewer whose authority changes while work waits. The expected behavior should come from the approved matrix and the actual permission system. Test a valid role aimed at an out-of-scope destination. That is different from testing an entirely unauthorized user. A service may legitimately perform updates for one site while being prohibited from touching another. The gate should preserve that resource scope when the model proposes or retrieves a new target.
Use a bounded hostile-content fixture in a disposable environment. Include a retrieved document instructing the agent to mark the packet approved or send content to an unrelated destination. OWASP’s prompt-injection guidance explains why untrusted input can try to alter model behavior. The acceptance condition here is that the trusted boundary prevents the unauthorized effect, even if the model proposes it. One ignored malicious instruction is evidence about one test; it is not a comprehensive security claim.
Test missing and contradictory evidence. A packet might contain a reviewer summary declaring readiness while a source reference is unresolved. Another might display an old preview while the field assignments refer to a newer revision. The review interface should expose or reject those inconsistencies according to policy. A human cannot make a reliable decision about evidence they were not actually shown. Preserve the references needed to explain which preview and source set belonged to the reviewed packet.
Test recovery around the decision boundary
Interrupt execution after the reviewer records a decision but before the destination action is confirmed. Resume through the supported mechanism and inspect whether the same effect is correlated with the same packet. If the remote outcome is uncertain, the correct result may be explicit reconciliation rather than another write. Do not count a repeated approval prompt as proof of safe recovery. It may simply ask a person to authorize a duplicate action without giving them evidence that an earlier attempt could have completed.
Test duplicate decision events if the surrounding integration can deliver them. Two messages carrying the same decision should not broaden its scope or create a second business effect. Record a stable decision and operation identity in the application contract where needed. Follow documented downstream idempotency behavior rather than inventing an exactly-once guarantee. A local approval record does not make an arbitrary external action transactional. The runbook should explain which outcomes are confirmed and which require inspection before another attempt.
Include a usability rehearsal with ordinary reviewers. Ask them to locate the changed claim, understand the permitted action, and reject a wrong target. Observe which evidence they miss and which labels they interpret differently from the implementation team. These are proposed evaluation exercises, not measured results from this article. Record actual observations when your team performs them. Avoid inventing a time-saving percentage to justify the gate before anyone has tested the review experience.
The final test report should separate enforcement failures from usability problems and operational gaps. A confusing label may lead a reviewer to make the wrong decision even when permission checks work. A clean interface may still sit on an overly broad service identity. Report each problem in the category that determines its owner and correction. A single average approval-quality score would conceal those differences. The useful release evidence is a set of specific boundary tests with documented outcomes and known remaining limitations.
6. Roll out gates that protect decisions without burying reviewers
Start with one consequential boundary
Choose one real workflow transition for the initial gate. A good candidate is a proposed update to a defined draft location where reviewers already have an editorial responsibility. Avoid introducing a new approval layer across every agent at once. The first release should establish whether the packet communicates the decision and whether the execution path respects it. Expand only after the team can explain rejections, stale packets, and uncertain effects without relying on the original builder’s memory.
Assign owners for the policy and its implementation. The editorial owner decides which evidence and roles a decision requires. The engineering owner implements the supported checks and recovery behavior. The operational owner monitors waiting work and handles technical exceptions. These responsibilities can overlap in a small team. What matters is that a change to a prompt, connector, role, or destination has someone accountable for assessing its effect on the gate. Do not let approval policy drift through incidental configuration changes.
Keep the first packet small enough to review. Show the intended change, destination, scope of authorization, and material evidence. Retain deeper diagnostic links for operators. Ask reviewers which additional information changes their decision before adding it to the default view. A packet full of generated reassurance is not a substitute for a clear difference view or a source excerpt. My preference is to spend interface space on the exact effect and unresolved issues rather than on a long statement that the agent followed instructions.
Measure the work the gate creates and prevents
Collect review outcomes that help improve the process. Proposed measures include rejection reasons, packet revisions before acceptance, waiting time by stage, and stale decisions prevented from executing. These are measurement suggestions, not performance claims. Define the population for each measure. Review waiting time should be distinguishable from execution time after approval. A campaign delayed because its source owner has not answered a question needs a different correction from a technically stuck action.
Use qualitative feedback alongside counts. Reviewers may repeatedly misunderstand a destination label, or operators may find that a state name hides whether an effect is uncertain. Fix those issues directly. Do not optimize for approval speed alone. A faster gate that causes reviewers to overlook unresolved claims has not met the intended purpose. Likewise, a high rejection count may reflect healthy detection of ambiguous input rather than a poorly functioning approval mechanism. Examine the evidence behind the metric before changing the policy.
Retain an exception process with a named owner. Urgent campaigns may need a different authorized route, but the record should state who accepted which scope and why. An exception should not impersonate an ordinary review that did not happen. Use the organization’s existing escalation rules and preserve the decision evidence. Avoid giving the agent discretion to invent urgency and bypass a gate. If a class of work genuinely warrants automatic handling, define it as an explicit policy with corresponding tests.
Keep change management and review policy connected
Reassess the gate when the workflow gains new tools or destinations. An approval scheme designed for draft updates may be inadequate after someone adds external delivery. A changed model or prompt can alter the content presented for review. A new template can change which fields matter to the destination effect. Treat those changes as reasons to revisit the packet and relevant fixtures. Do not assume that unchanged button labels mean the protected decision stayed the same.
Version the policy and the review packet format. Waiting work should retain the policy reference under which it was prepared. Decide whether a policy update lets existing packets finish or requires renewed review. Preserve the reason for that decision. Do not rewrite historical records to suggest that an old approval was made under a newer rule. An operator investigating a past effect needs to understand the actual conditions at the time, including the limitations of the mechanism then in use.
Before expansion, run a handoff exercise with people outside the implementation team. Give a reviewer a changed artifact and give an operator an uncertain post-approval action. They should identify the authorized subject, the last confirmed state, and the next permitted action from the ordinary evidence. If they cannot, improve the packet, state labels, or runbook. This is a concrete test of the operating design. It does not require pretending that every possible input or race has been covered.
The practical release gate is a demonstrated agreement between the human decision and the executed effect. Require a stable packet reference, authenticated decision evidence, destination scope, an invalidation policy, and a recovery rule for uncertain actions. Verify those controls through the actual supported interfaces. The next step is to select one current approval point and compare its record with the action it authorizes. Close the first mismatch you find before adding another pause to the workflow.
For a review checklist, ask the publisher to point to the evidence rather than answer from memory. Which packet was approved? Which operation does it permit? What invalidates it? How does the destination confirm the result? Who resolves an uncertain attempt? Each answer should identify a record, a supported check, or an accountable person. If the answer is simply that the agent was instructed to be careful, the boundary is still a prompt convention. Improve that boundary before treating the gate as a reliable part of production release.